Smart Contract Risks on a DEX: What to Know in 2026
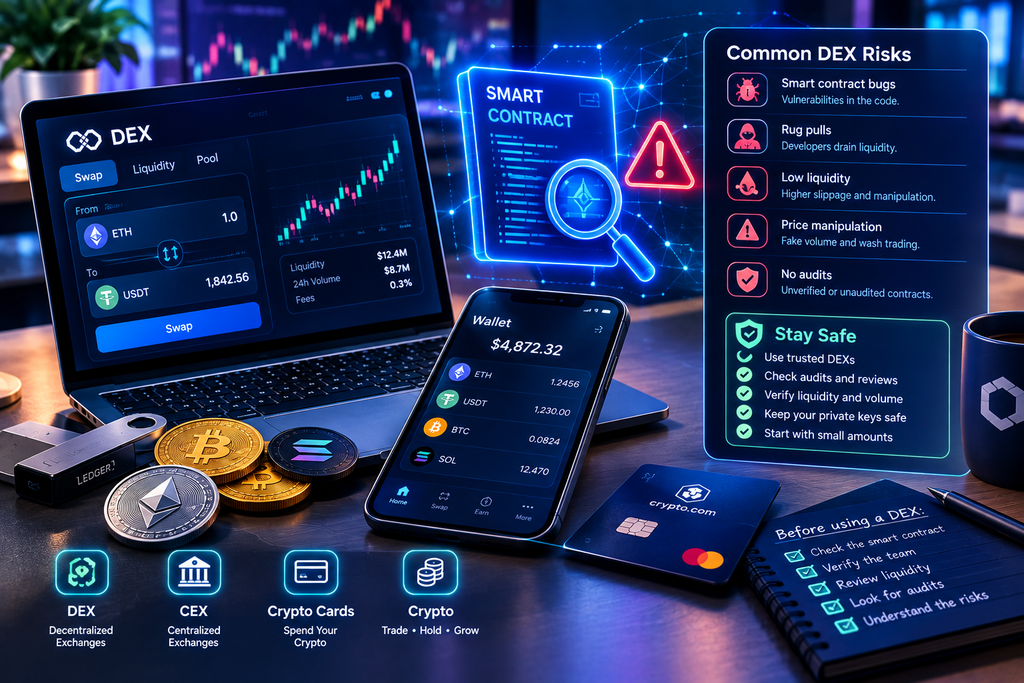
Trading on a DEX means trusting code instead of a company. Understanding smart contract risks is what separates a safe experience from a costly one. In April 2026 alone, DeFi protocols lost more than $600 million to exploits, making it one of the worst months on record. This guide breaks down what’s actually causing these losses, how the attacks themselves have changed, and what you can realistically do to protect your funds.
The Numbers Are Actually Getting Worse in 2026
DeFi protocol losses fell sharply in 2025, dropping 74% from their 2022 peak to around $680 million for the full year. However, 2026 reversed that trend fast. April 2026 alone recorded over $600 million in losses, driven by a small number of massive individual incidents. The largest single breach that month, a roughly $293 million drain at Kelp DAO, accounted for a huge share of the total on its own.
Here’s the Twist: It’s Not Always the Code That Fails
This is the detail most beginners miss entirely. Three of the four largest DeFi incidents in 2026 didn’t involve a flawed line of code at all. Instead, attackers gained access they shouldn’t have had. They then instructed otherwise-functioning smart contracts to do exactly what they were told. In one striking case, North Korean state-linked hackers spent six months building trust with a Solana-based DEX’s team through social engineering. As a result, they gained privileged administrative access, then used it to introduce a fake asset and drain real funds within hours.
This shift shows up in the broader data too. Phishing and social engineering now account for more than half of all DeFi breaches. In fact, they’ve actually surpassed traditional technical vulnerabilities as the leading cause of losses. So, the biggest smart contract risk today often isn’t a bug in the contract itself. Instead, it’s the human being who holds the keys to change it.
The Technical Risks Still Worth Understanding
That said, genuine code-level vulnerabilities remain common and dangerous. According to the industry-standard OWASP Smart Contract Top 10 for 2026, access control failures rank as the single most common vulnerability category. These typically involve exposed admin functions or weak permission checks that let attackers seize control of a contract outright. Price oracle manipulation ranks close behind, where attackers distort the price data a protocol relies on to trigger favorable, fraudulent transactions.
Reentrancy attacks, one of the oldest tricks in DeFi, still show up regularly too. This happens when a contract makes an external call before updating its own internal state. Because of this, an attacker can repeatedly withdraw funds before the contract realizes anything is wrong. Integer overflow bugs, where a calculation produces a number too large for the system to handle correctly, caused a $26.4 million loss at one protocol in a single incident early in 2026.
Bridges Got Safer, But Aren’t Risk-Free
One piece of genuinely good news: cross-chain bridges, once responsible for the vast majority of DeFi losses, now account for a much smaller share of total incidents than they did in 2022. That said, bridges still carry real risk. This is especially true when they rely on a single validation method rather than multiple independent checks, a weakness attackers have specifically targeted in more recent incidents.
How to Actually Protect Yourself
Since human error and social engineering now drive more losses than raw code bugs, your own security habits matter more than ever. First, be skeptical of unsolicited contact, even from people who seem to represent a legitimate team, since sophisticated attackers now invest months building trust before striking. Next, regularly review and revoke token approvals you’ve granted to old or unused DeFi protocols. A forgotten approval to a contract that later gets hacked can put your funds at risk even without any action on your part.
In addition, favor protocols with a strong audit history from a reputable firm. However, don’t treat an audit as a permanent guarantee. A protocol’s code and dependencies change constantly, and even mature, long-running programs eventually surface new critical vulnerabilities. For official technical guidance on the most common vulnerability categories, see the OWASP Smart Contract Top 10.
Weighing This Against Centralized Alternatives
None of this means DEX platforms are inherently worse than centralized exchanges. Each model carries a different kind of risk. We cover that trade-off directly in our guide to CEX vs. DEX, and how upcoming stablecoin regulation is separately reshaping both types of platforms in our guide to DeFi and the GENIUS Act.
The Bottom Line
Smart contract risks in 2026 look different than they did just a few years ago. Technical bugs like reentrancy and oracle manipulation still cause real damage. However, the fastest-growing threat is human, not technical: social engineering and compromised access now drive more losses than flawed code alone. Protecting yourself means combining the usual technical caution, checking audits and understanding what a protocol actually does, with genuine skepticism toward anyone requesting access or trust, no matter how legitimate they appear.
FAQs
What is the most common smart contract vulnerability in 2026?
Access control failures currently rank as the most common category, according to the OWASP Smart Contract Top 10, typically involving exposed admin functions or weak permission checks.
Are DeFi hacks caused mainly by bad code?
Not anymore, necessarily. Phishing and social engineering now account for more than half of all DeFi breaches, surpassing traditional code-level vulnerabilities as the leading cause of losses.
What is a reentrancy attack?
It’s an exploit where a contract makes an external call before updating its own internal records, allowing an attacker to repeatedly withdraw funds before the contract registers the change.
Does an audit guarantee a DeFi protocol is safe?
No. An audit reflects a point-in-time review, but protocols change and add new dependencies over time, meaning even audited, long-running programs can surface new vulnerabilities later.